Configure network policies
FydeOS Management Cloud deploys managed network settings as Open Network Configuration (ONC) JSON. Use ONC when devices need a preconfigured Wi-Fi, Ethernet, VPN, proxy, DNS, or certificate-backed connection.
Before you begin
- Create a pilot organisational unit and move one representative device into it.
- Keep a working fallback network available during testing.
- Collect the SSID, security type, EAP method, identity format, VPN or proxy details, and certificate requirements.
- Decide whether the connection is for signed-in users or for another device stage. The console currently states that network restrictions apply only after users sign in.
- Store passphrases and private keys using your organisation's approved secret process. Do not place production credentials in screenshots or tickets.
Choose the right configuration
| Requirement | Start here |
|---|---|
| WPA/WPA2/WPA3 personal Wi-Fi | Configure Wi-Fi with ONC |
| PEAP/MSCHAPv2 or EAP-TLS Wi-Fi | Configure Wi-Fi with ONC |
| Ethernet, static IP, VPN, or per-network proxy | Configure Ethernet, VPN, and Proxy |
| User/device placeholders and reusable JSON | ONC Variables and Examples |
| Certificate upload and renewal | Manage Certificates |
| A managed network does not work | Troubleshoot Managed Networks |
Publish an ONC change
- Open Business+ → Network Configuration.
- Select the pilot Organisational Unit.
- Copy the current ONC to your change record before editing it.
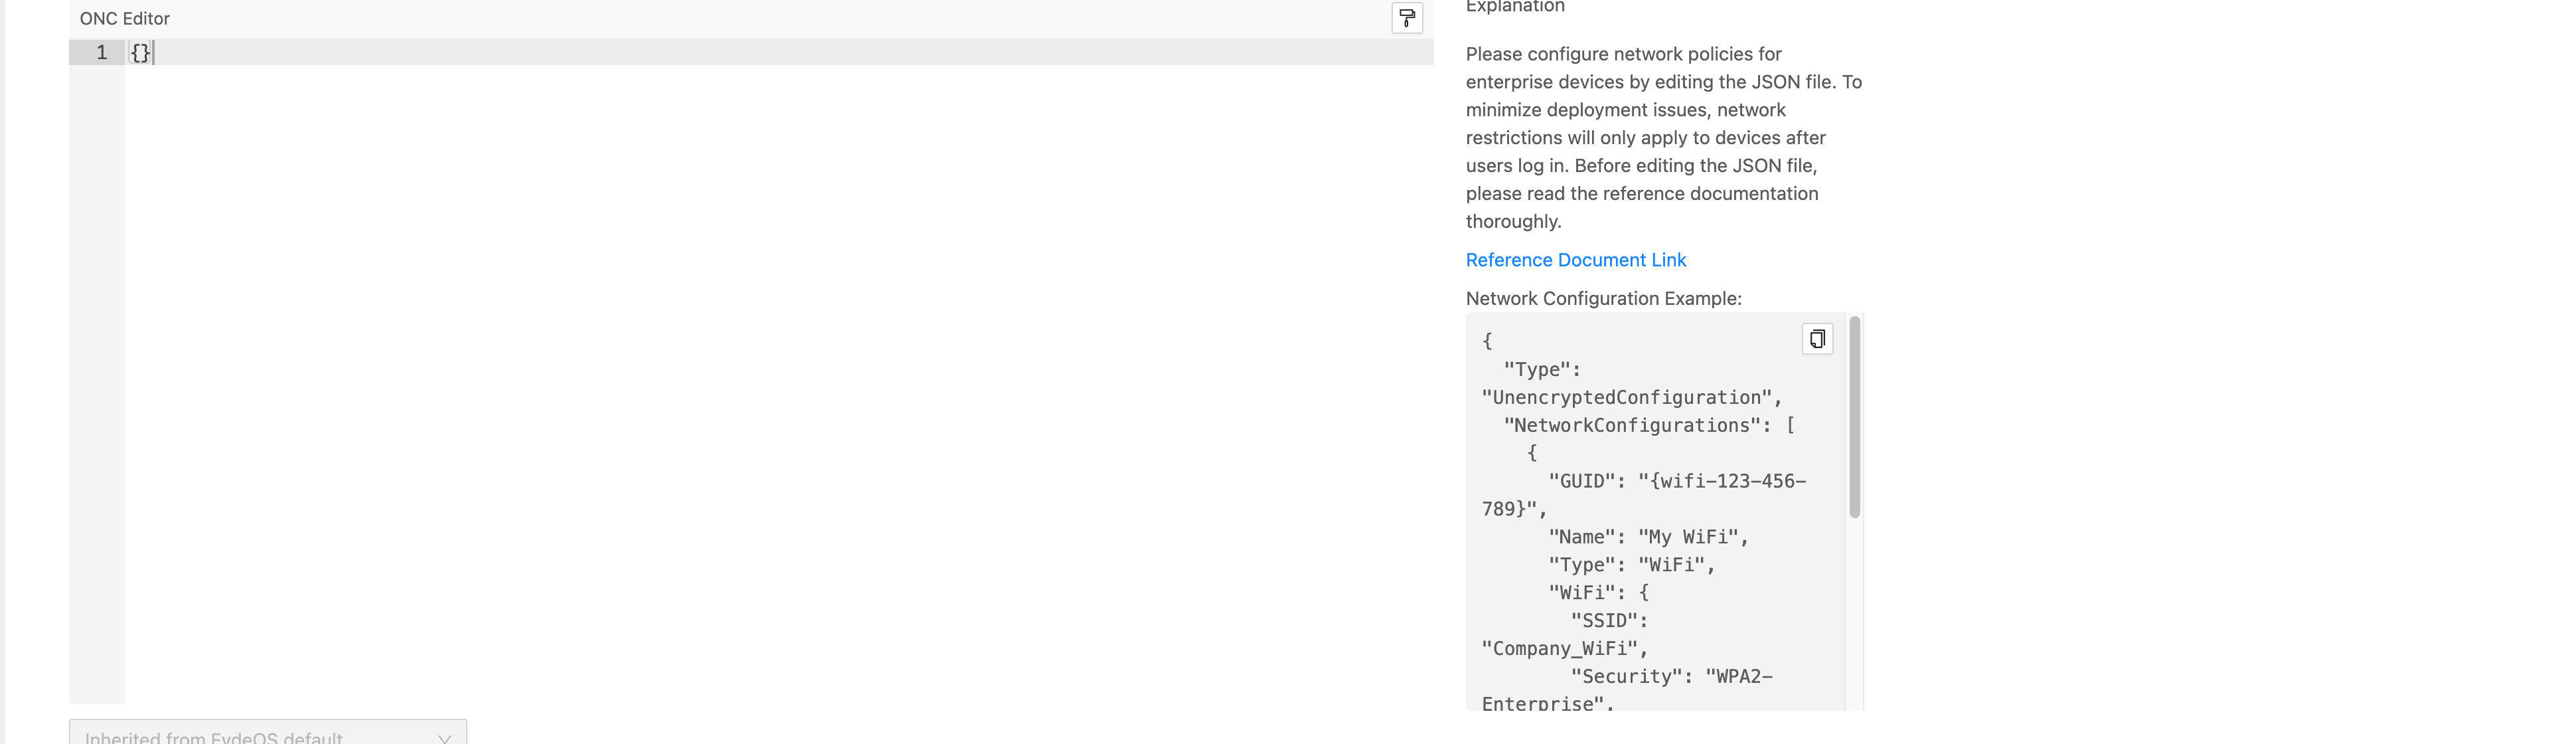
- Edit the complete JSON document in ONC Editor. The top-level type for a
normal policy is
UnencryptedConfiguration. - Use the formatter button and check brackets, commas, quotes, and field types.
- Confirm that every network and certificate has a stable, unique
GUID. - Review the applied or inherited state shown below the editor.
- Save the policy if the page presents a save action. Do not switch units until the change is complete.
Sign-in and enrolment connectivity
Management Cloud explains that its network restrictions apply after users log in. Do not assume this policy will provide first-boot or enrolment connectivity. Keep an enrolment network available until a pilot has completed enrolment, sign-in, policy sync, and restart testing.
How ONC updates work
- A
GUIDidentifies one network or certificate. Keep it unchanged when updating that same object. - Use a different
GUIDfor every distinct object, even when names are similar. - Set
"Remove": trueand provide only the existingGUIDto remove an imported network or certificate. - Any certificate referenced by GUID must be included in the same ONC document.
- Replacing the editor content with
{}removes the definitions from that policy document. Treat this as a production change, not as a harmless reset. - Child organisational units can inherit a parent configuration. Check the selected unit and the inheritance state before diagnosing the JSON.
Pilot and verify
- Apply the configuration to a pilot unit.
- Sign in on the pilot device and allow time for policy sync.
- Confirm that the expected network appears and connects automatically only when intended.
- Test IP assignment, DNS, captive portal handling, proxy routing, internal resources, and public internet access.
- For enterprise authentication, verify the identity value and server certificate chain.
- Restart and test sign-in again.
- Test rollback by restoring the saved previous JSON.
- Expand to production units in stages.
For every field and supported object type, use the Open Network Configuration reference.
What's next
- Manage certificates, prepare trust anchors and client certificates.
- Troubleshoot managed networks, diagnose policy and connection failures.
- ONC reference, look up schema fields and accepted values.